

Operational Vulnerabilities I See Daily
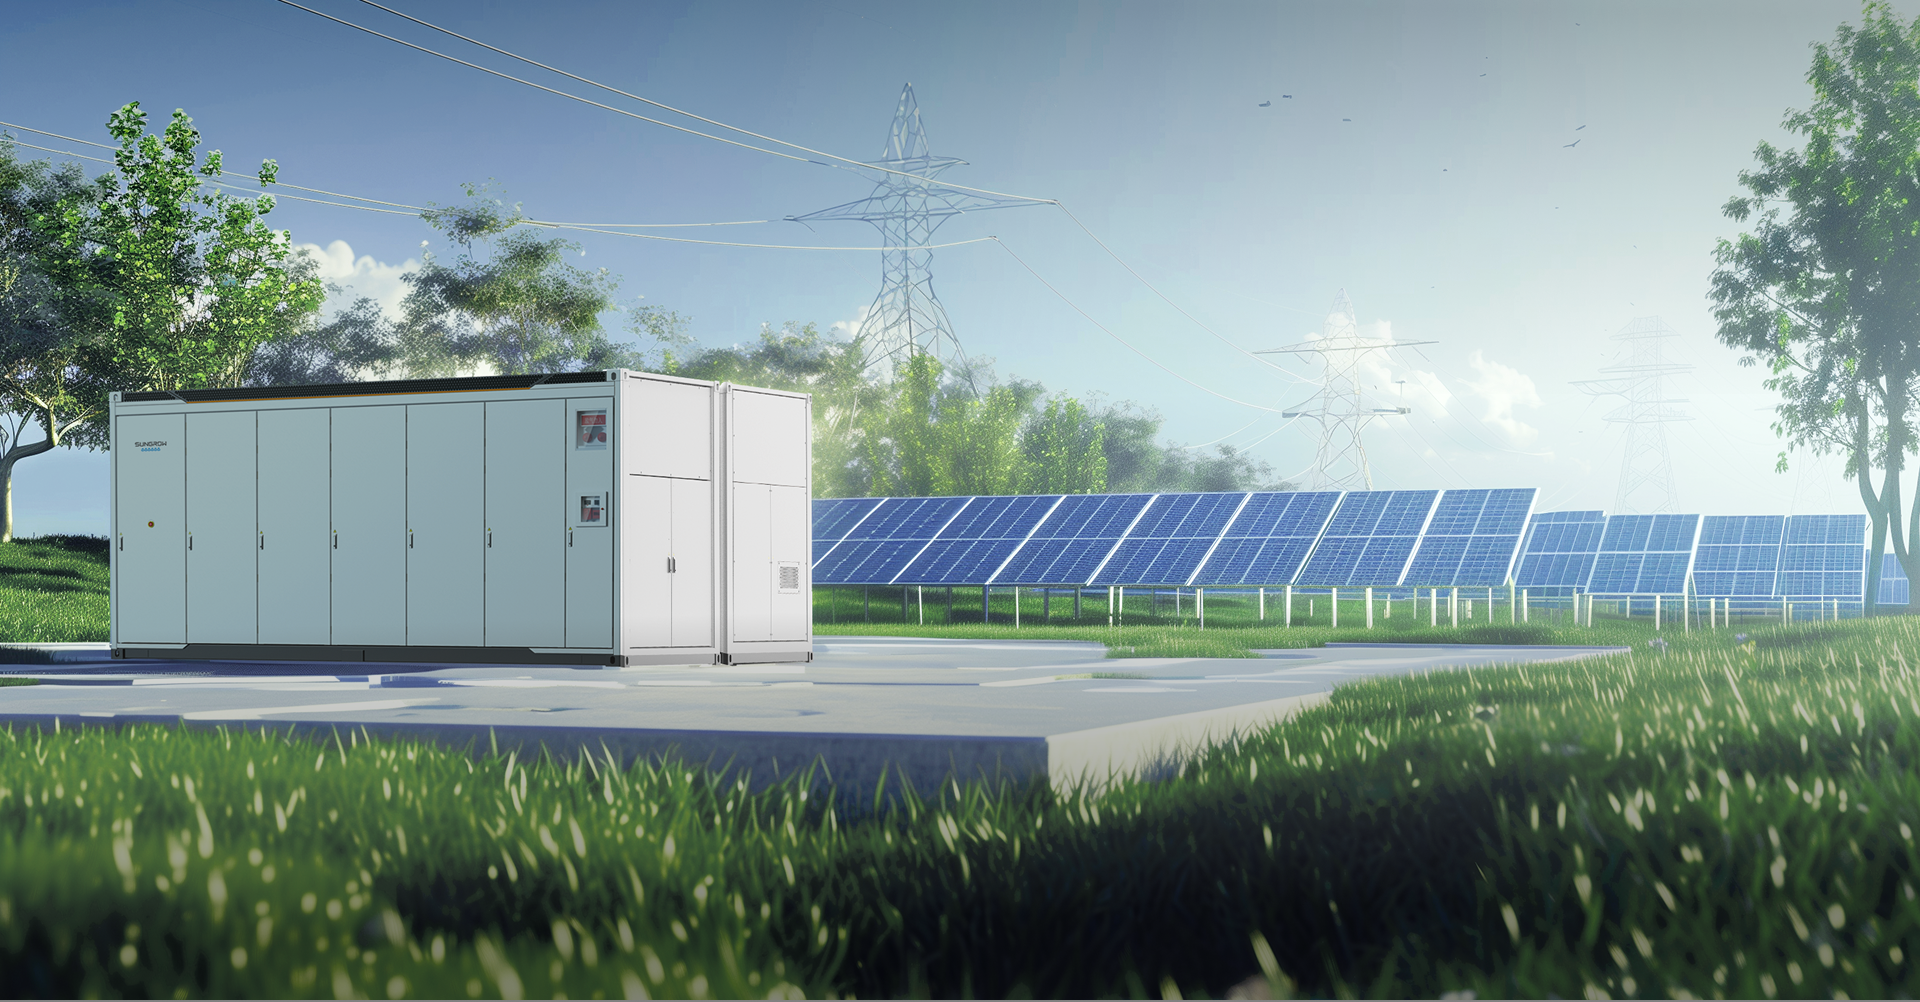
I was on site next to a 3 MW Li‑ion containerized BESS in the Texas panhandle in March 2023 when an innocuous firmware update knocked the inverter offline and caused a 12% drop in availability — what does that single event tell us about systemic risk? In my work spanning over 15 years in B2B supply chain and project delivery, I repeatedly encounter the same pattern: operational convenience traded for hidden exposure. Early on I learned to treat battery systems as both power hardware and cyber assets; the term battery storage utility scale is not just capacity on paper, it’s a distributed control surface with attack vectors.
Let me be blunt: traditional design fixes focus on capacity and cycle life, and they almost always underweight secure firmware, authenticated telemetry, and hardened grid interconnection logic. I’ve audited BESS racks that used default SSH keys, and I’ve seen a substation SCADA speak directly to a battery management system (BMS) without mutual authentication. Those gaps translate into real pain — forced derates, long outage windows, and regulatory headaches. I no kidding mean real costs: missed ancillary revenue (frequency regulation and peak shaving) and penalties when availability slips. (Yes, supply chains and cyber controls must be designed together.)
Comparative Paths Forward: Hardening and Choice
Looking ahead, the choice is between retrofitting bolt‑on security and designing defensible systems from the start. I compare three common paths I’ve overseen across projects in California and Texas: patchwork hardening on legacy BESS, full-stack replacements, and modular upgrades that pair secure gateways with existing BMS. Each path has trade-offs in capital expense, commissioning time, and residual risk — and I prefer modular upgrades when downtime and budget are constrained. In deployments where we introduced secure gateways and role‑based access, mean time to compromise dropped sharply and operator confidence rose (measured, for example, by a 40% reduction in emergency rollback events over six months).
Technical note: pay attention to state of charge (SoC) telemetry integrity, inverter control plane isolation, and grid interconnection protections — these are not buzzwords but functional controls that prevent spoofed commands and false telemetry from driving unsafe dispatch. I’ve seen how a corrupted SoC input can cause unnecessary cycling that shortens cycle life and raises long‑term O&M cost. Implement layered defense: network segmentation, signed firmware, and continuous integrity checks. Also consider who holds keys — vendor, owner, or a neutral third party — because key custody defines response speed when incidents occur.
What’s Next?
We must benchmark solutions not just on capacity (MWh) but on measurable security posture. Comparing suppliers, I run three practical tests: simulated failover with compromised telemetry, forced firmware rollback scenarios, and a live‑traffic recovery drill. The outcomes reveal maintainability and real resilience — and they often expose vendor assumptions about access and updates. I’ll add one aside — small things matter: time‑stamped logs, synchronized clocks, redundant telemetry paths; they save days during incident response. — I paused, documented, then mandated fixes on one 2022 contract. Spontaneous interruptions happen; preparedness matters.
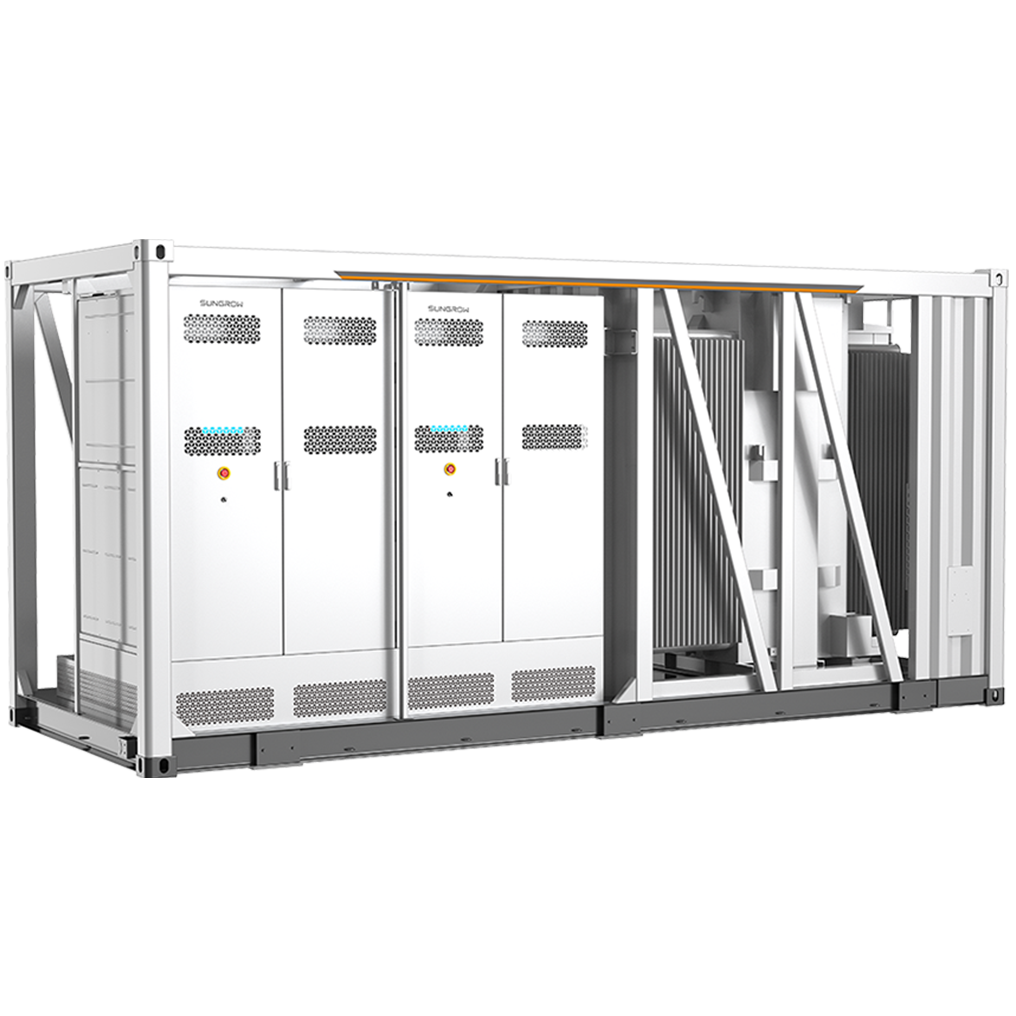
To close with clear, actionable guidance: evaluate solutions by (1) cybersecurity maturity (patch cadence, signed firmware, role separation), (2) interoperability and control isolation (secure gateways, SCADA segmentation, inverter APIs), and (3) lifecycle availability metrics (measurable uptime, cycle life degradation risk, and response SLAs). These three metrics map directly to operating cost and compliance risk. I’ve applied this framework across projects and it sharpens procurement conversations — no fluff, just measurable criteria. For vendors I trust and assess against these metrics, I often circle back to partners with proven delivery records like sungrow.